HiddenLayer: An Overview of AI Model Security and Technology
HiddenLayer delivers comprehensive security, visibility, and governance for artificial intelligence models, safeguarding corporate infrastructure from emerging threats throughout the entire AI lifecycle.
HiddenLayer: Securing the AI Model Era: As companies adopt a growing number of artificial intelligence models, cybersecurity requirements are shifting away from legacy software defense. HiddenLayer concentrates explicitly on safeguarding AI models, agent networks, and operational workflows from emerging risks. Its system delivers comprehensive governance, visibility, and protection throughout the entire artificial intelligence lifecycle.
Why AI Models Need Security: Artificial intelligence models can harbor concealed elements, malicious alterations, and structural vulnerabilities that standard security utilities frequently overlook. According to HiddenLayer, conventional application security methods lack the capability to properly interpret neural networks. This introduces distinct security hurdles as enterprises grow increasingly dependent on open-source and third-party models.
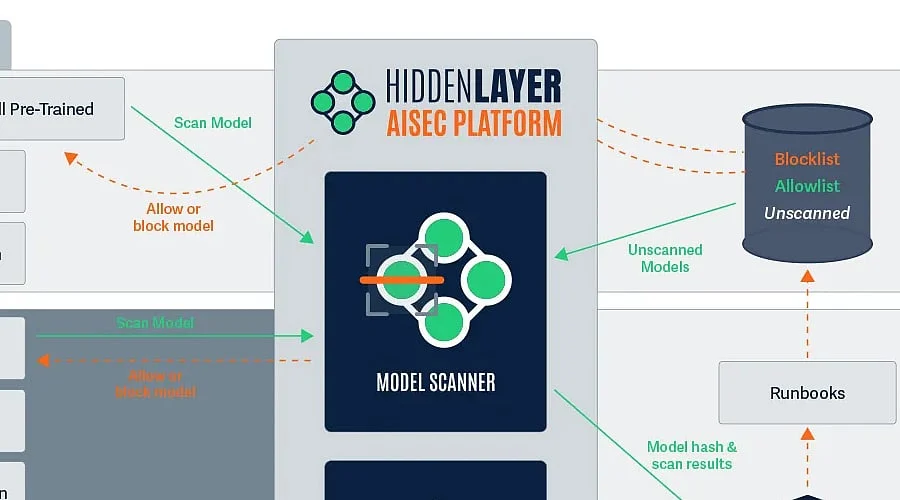
AI Supply Chain Security: HiddenLayer evaluates AI models prior to corporate implementation in production environments. The technology analyzes model weights, layer configurations, architectures, and associated files to detect any irregularities or tampering. Furthermore, it records model lineage, enabling businesses to trace the origin of models and understand their derivation.
AI Discovery: The software pinpoints artificial intelligence assets throughout a company’s infrastructure, encompassing unsanctioned or “shadow AI” rollouts. Consequently, security personnel gain oversight of workflows and models that might otherwise elude monitoring. Such transparency ultimately bolsters risk management and administrative governance.
Runtime AI Protection: Protection does not conclude once an artificial intelligence model enters production. The runtime security solutions from HiddenLayer actively identify and mitigate AI threats during active system operations. The platform specifically defends against data leakage, unauthorized tool operations, model extraction, and prompt-based attacks.
Red Teaming AI Systems: To evaluate systems against shifting dangers, HiddenLayer provides AI attack simulation services. By conducting red-teaming exercises, organizations can uncover flaws before malicious actors exploit them in live settings. Ultimately, continuous evaluation of agentic networks, applications, and models aims to enhance overall AI resilience.
Governance and AI Guardrails: Securing artificial intelligence also mandates established regulations regarding model behavior and operational usage. HiddenLayer supplies guardrails and governance controls designed to enforce compliant and secure operations. Enterprises leverage these tools to oversee risk across diverse business units and models.
Join our WhatsApp Channel to get the latest news, exclusives and videos on WhatsApp